Passwords Aren’t Enough! Secure Your Online Accounts Now.
How does Multi-factor verification help to protect your online accounts from hackers, scammers and prying eyes and how do you go about setting it up?
📌 Key Takeaways: Multi-Factor Authentication at a Glance
- Why Passwords Aren’t Enough: Over 80% of data breaches involve weak, reused, or stolen passwords. MFA adds vital extra layers of protection.
- The Three Security Pillars: Authenticators verify identity using something you know (passwords), something you have (phones/keys), and something you are (biometrics).
- Apps & Keys Beat SMS: While SMS text codes offer a basic layer of defence, authenticator apps and physical security keys provide far superior resistance against phishing and interception.
- Quick Setup: Enabling MFA on critical business email, VoIP setups, and banking accounts usually takes less than two minutes.
Table of Contents
Why Passwords Alone Are No Longer Enough
The main weakness of passwords is that they’re a single layer of protection for your accounts.
Passwords on their own can be ridiculously easy to bypass for a determined hacker.
An all to common and sophisticated method hackers use is to conduct a phishing scam where the hacker sends you an email that looks like a legitimate email for one of your accounts and asks you to click a link and sign in. They design a fake page to look like the account you’re trying to sign into, but as you make an attempt to sign in, you unwittingly gave your password to the hacker.
Another method could just be that person wanting to hack you could simply be looking over your shoulder as you’re typing a password. Not as uncommon as you might think – disgruntled co-workers, people working in coffee shops etc.
Of course, if you have a rubbish password, then there’s no excuses…
Most people’s passwords
Security experts recommend we make our passwords as long as possible (9 characters or more), adding in capital letters, numbers and special characters to make our passwords stronger. Most people however, do use simple-to-remember words or phrases with some extra punctuation or flourishes in there to make them harder to guess, but unfortunately this is still leaving yourself open to being hacked.
It’s a given that you need to make your passwords strong, but in the real world we all need to remember those passwords for our day to day accounts and unfortunately not everyone is using a Password Manager yet.
As we’ve mentioned, there are lots of creative and nefarious ways a hacker or scammer can do to get hold of your password, so without two-step verification, once someone has your password, they can easily get into your accounts and cause all sorts of personal, reputational or financial damage.
Worse still, if you’ve used the same password for other online services (don’t do this!), then it really doesn’t take a determined hacker much work to log into to all of your other accounts to find out more about you, which websites you use, who your friends are, etc etc. Easy identity theft 101.
The 3 Types of Authentication Factors
Two step verification is essentially adding a second layer of security on top of your password to protect your accounts.
At the heart of all Multi-Factor Authentication are the three fundamental pillars of identity verification:
- Something You Know: Information only you should possess, such as a password, PIN, or response to a security question.
- Something You Have: A physical item or registered device, such as a smartphone receiving an app notification or a USB hardware key.
- Something You Are: Unique physical characteristics verified through biometrics, like a fingerprint scan, facial recognition, or voice pattern.
True MFA requires combining methods from at least two of these distinct categories, making it significantly harder for unauthorised users to compromise your account.
In practice, in order to sign in to your account the website not only asks you for something you know (your username and password), but also asks you either for something you have, such as your mobile phone to send a text code to, or, something you are, such as a fingerprint, facial recognition or voice print.
The thought behind this is that IF your password has been compromised, then the hacker, wherever they are in the world, still can’t access your account because they wouldn’t have the second part of the login process to enter your account, be that code, fingerprint, hardware key, or face recognition.
For further security, 2fa verification codes are time limited – they expire after a short period and can only be used once however you can always ask for another code if you didn’t enter the first one in time.
How you would log in to an online account with two-factor authentication enabled
- Enter your username & password
- The website detects the login attempt so requests you to verify yourself.
- You verify your identity with a separate 2fa code, physical 2fa key, or biometrics (fingerprint, face recognition) then you’re in.
Quick Tip: Understanding the Terms
While Two-Factor Authentication (2FA) and Two-Step Verification (2SV) require two checks to confirm your identity, Multi-Factor Authentication (MFA) is the umbrella term for using two or more security steps—though in practice, all three terms are often used interchangeably to describe adding an extra layer of protection beyond your password.
Common MFA Methods Compared (SMS vs. Apps vs. Hardware Keys)
| Authentication Method | Security Level | Ease of Use | Best For |
|---|---|---|---|
| SMS Text Verification |
Basic Vulnerable to SIM swapping and interception |
Very Easy No app setup required |
Casual personal accounts and users without smartphones |
|
Authenticator Apps (e.g. Google or Microsoft) |
High Generates time-sensitive codes locally |
Easy Simple QR code setup |
General business logins, daily personal accounts, and remote teams |
|
Biometrics & Passkeys (e.g. Face ID, Touch ID, Windows Hello) |
Very High Phishing-resistant device-bound credentials |
Extremely Easy Instant facial scan or fingerprint tap |
Quick passwordless unlocks, modern smartphones, and corporate laptops |
|
Hardware Security Keys (e.g. YubiKey) |
Maximum Phishing-resistant physical key |
Moderate Requires physical key insertion or NFC tap |
Admin accounts, sensitive business data, and enterprise security |
SMS Text message
The simplest way to enable two factor authentication is via your mobile phone.
Within your online account settings, you will need to provide your mobile phone number.
As you try to log in to your account, you will be sent a code via SMS to log into your account.
Every time you want to get into your account, you get a new code sent to your phone. Most verification codes expire in a matter of minutes, providing that extra level of security for you.
Caveat
Having multi-factor codes texted to your phone is a great first step into using multi-factor authentication, however it isn’t infallable. Nothing is. There are ways for very determined hackers to clone mobile numbers, or spoof multi-factor authentication pages, so if your account is of particular high value, then you should look below at authenticator apps or hardware keys instead – they are just as easy to use and offer better overall security.
The above being said, you should absolutely have sms multifactor enabled if you have no other multi-factor options available, text multi-factor is infinitely better than not having it enabled so if you just need a simple option to get you started with your account security, then absolutley enable it now!
Authenticator Apps
The next step up from using text messages to get your authentication codes is to use an app.
Without getting too technical, what the apps do is generate an encryption key between your device and the service in question that allows them both to generate the same code independently of each other. This means that even if you don’t have mobile signal to receive an sms text message, you can still get your authentication code.
With nothing being sent via text here, there’s no danger of your phone number being cloned or spoofed, so that extra hole is shut for hackers here.
The popular Lifehacker blog has listed the best authentication apps for both iPhone and Android devices. Personally I use the Google authenticator app, it allows me to generate codes for all of my online accounts, Facebook, AWS, Google, etc etc but in principle most authenticator apps work in the same way.
How to set-up an authenticator app
In your online account, when you click the option to set up multi-factor you will be shown a QR code on your computer screen.
Within your authenticator app on your mobile phone, you click to add a new code, then scan the code on the screen.
You will be shown your new code with a timer next to it, showing when it expires – your online account will ask you to verify the code you see on your mobile phone to confirm everything is working and that’s it, you’re good to go!
Biometric Authentication & Passkeys
Representing the third pillar of security, something you are, biometric methods allow you to verify your identity using physical characteristics, such as a fingerprint scan (Touch ID), facial recognition (Face ID or Windows Hello), or iris scans.
In modern security setups, biometrics are rarely transmitted over the internet. Instead, modern systems use device-based biometric verification to unlock an underlying cryptographic credential (often referred to as a passkey). Your phone or computer confirms your identity locally on the device, unlocking access without sending sensitive biometric data or passwords across the web.
Biometric devices can include:
- Finger print readers
- Webcams with an IR light emitter, and a specific filter that can read infrared light and sense depth in 3d space. You will often see these webcams listed as “Windows Hello Compatible”
Key Advantages:
- Phishing-Resistant: Because there is no typed password or manual code to intercept, attackers cannot trick you into entering credentials on fake login pages.
- Unmatched Speed & Convenience: Logging in takes seconds with a simple glance or fingerprint tap, eliminating password fatigue.
- Zero Shared Secrets: Your biometric data remains stored within a secure enclave on your device and is never shared with third-party websites or external servers.
Hardware Authentication Keys
The pro way of doing two-step verification.
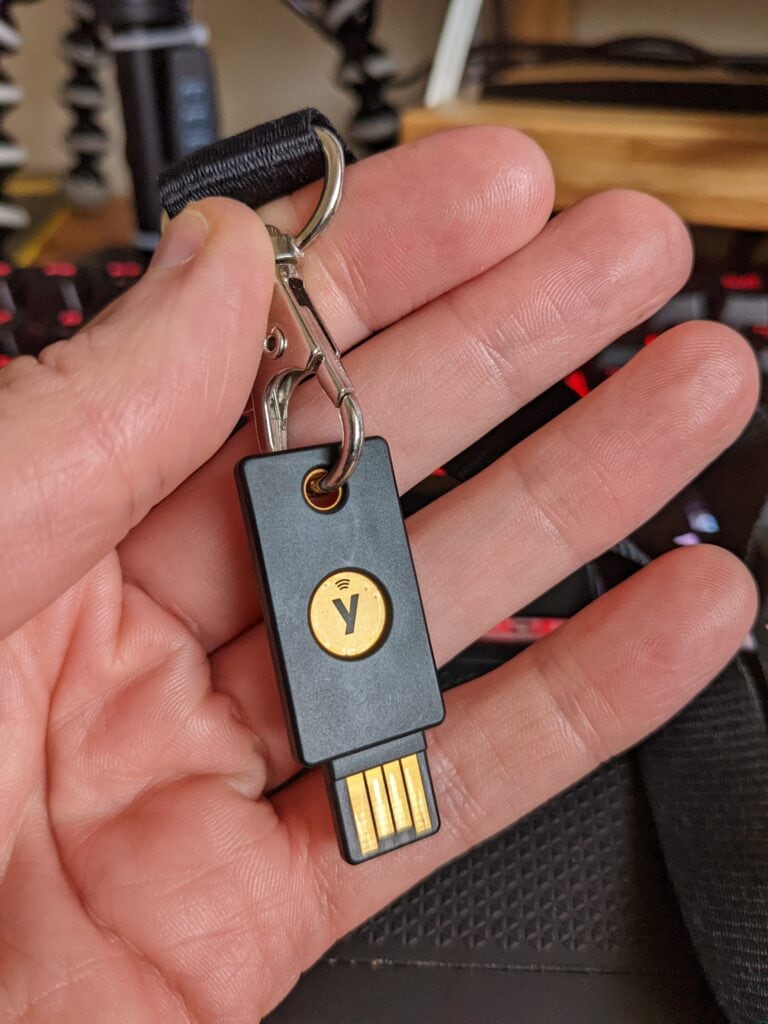
A hardware authentication key is a physical key you can plug into your computer to confirm you are the account holder of whichever accounts you have registered with that key.
This isn’t as complicated as it sounds, they’re simply like having house keys, plus spares.
If you’re not convinced, please enjoy this cheesy 30 second video from the guys at Yubikey.
Whichever accounts you’re wanting to protect, you simply register your hardware key, or keys (like your house keys, it’s good to have a spare set) with your account so that going forward, to log into those accounts, you will need to have your key with you to log in.
It’s worth noting that some keys are compatible with NFC so you can use them with your mobile phone to simply touch the device and log in to your account.
Where can I get a Hardware Authentication key from?
There are lots of companies making hardware keys so they’re quite readily available – I have a Yubikey, but I also hear good things about Google’s titan, TrustKeys and Project Telecom keys – all linked below.
- 2FA Keys by Yubikey
- Google Titan 2FA Authentication Keys
- TrustKey authentication keys
- 2FA Authentication keys by Project Telecom
Key takeaways
- SMS offers a solid baseline but is increasingly targeted by hackers through SIM swapping.
- Authenticator Apps strike the ideal balance of strong security and convenience for everyday business use.
- Biometrics (such as Face ID or fingerprint scans) provide fast, convenient security by relying on unique physical traits, making them ideal for mobile devices and fast account access.
- Hardware Keys offer top-tier security for critical accounts and IT environments where passwords alone pose a high risk.
What if I lose my phone or key?
As part of most two-step verification set-ups, you can use multiple methods of two-step verification so you can set-up backup telephone numbers, email addresses or keys, so you’ll never find yourself locked out of your account. Google even lets you print out a set of single use only verification codes to keep in a safe place as a further backup.
Always have backups or spares
Like having spare keys for your house, it is worth noting that the more backups or spares you have the more you will need to be aware of where those spares, or backups are.
Nobody can tell you how many backups you will need, that is down to your personal preference and risk management, but you should probably have at least one backup method of logging in.
Google explain more here:
If you lose a key, or change your phone number, remember to log into your accounts and remove those methods of verification from your account and update to your new two-factor details.
How to Set Up an Authenticator App
I’ve collected links to the help pages from some of the most popular online services here which describe how to set-up two-factor authentication on their services using one or multiple methods as described above.
Google, Gmail, YouTube etc
Google two-factor authentication page describes really well what it is and how it works.
Instructions on how to enable two-factor authentication for your Facebook account
Microsoft Office – Hotmail, Live etc
Find out more on using two-step verification for Microsoft services here. Microsoft has its own code generator app for its services.
Paypal
If you want to enable two-factor authentication for your Paypal account, you can enable it quite easily, but only text messaging is supported at the time of writing this blog.
Linked in
How to set-up to factor authentication on your Linked in Profile.
How to set-up two-factor authentication for Twitter
How to set-up two-factor authentication on Instagram
In summary:
Enable two-factor authentication on all of your online accounts now!
From a personal stand point, I’ve been trying hard to advise friends and family to use two-step verification, but it’s an uphill struggle, it all seems more complicated than it actually is. It’s really not, and this is part of the reason why I wrote this blog, so I can say “Look, I actually took time out at work to write this! It’s really important. You should know about this.”
You’ll all be making this PMC blogger a very happy guy if you look at two-step verification!
You should have this enabled on all of your accounts!
Improving your passwords
If after all of this you still don’t want to use two-factor authentication, then you definitely should look at how you can improve your passwords, yet keep them easy to remember.
Computerphile have a superb video here that explains in detail just how to do that.
Frequently Asked Questions About Multi-Factor Authentication
What is Multi-Factor Authentication (MFA)?
Multi-Factor Authentication (MFA) is a security process that requires users to provide two or more distinct verification factors to gain access to an account or system, adding an essential extra layer of defence beyond just a password.
What is the difference between 2FA and MFA?
Two-Factor Authentication (2FA) specifically requires exactly two authentication steps (such as a password and a code), whereas Multi-Factor Authentication (MFA) is the broader term covering two or more verification steps. In everyday practice, both terms are often used interchangeably.
What are the three core pillars of authentication?
The three pillars of authentication are: something you know (such as a password or PIN), something you have (such as a mobile phone, authenticator app, or hardware key), and something you are (biometrics like fingerprints or facial recognition).
Are SMS verification codes secure for MFA?
While SMS text codes are better than relying on passwords alone, they are vulnerable to interception techniques such as SIM swapping. Authenticator apps (like Google or Microsoft Authenticator) or physical hardware keys (like YubiKey) offer significantly stronger protection.
Why is a password alone no longer sufficient for business security?
Passwords can be stolen, guessed, or exposed through data breaches and phishing attacks. Requiring a secondary verification factor ensures that even if an attacker acquires your password, they still cannot access your account without your physical device or biometric data.